 |
10Duke Enterprise C++ SDK
|
|
10Duke Enterprise C++ SDK
|
#include <JWTSignatureValidator.h>
Service for validating the JWT-signature.
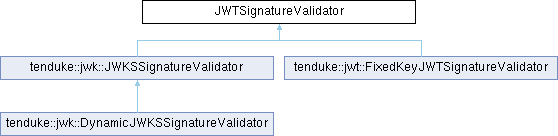
Public Member Functions | |
| virtual bool | validate (const tenduke::json::JSONObject *jwtHeader, const char *payload, std::size_t payloadLength, const unsigned char *signatureBytes, std::size_t signatureLengthB) const=0 |
| Validates JWT signature. | |
| virtual std::vector< std::shared_ptr< const tenduke::crypto::PublicKey > > | getVerificationKeys () const |
| Returns the public keys, which the validator currently trusts for verifying signatures. | |
|
inlinevirtual |
Returns the public keys, which the validator currently trusts for verifying signatures.
The keys can be stored to verify the signatures later, e.g. when there is no network connection. The keys come from memory: this method never loads keys over the network.
The default implementation returns no keys, for validators which cannot provide them.
|
pure virtual |
Validates JWT signature.
| jwtHeader | JWT-header, can be e.g. used to determine the key and digestAlgorithm used |
| payload | JWT-payload to verify |
| payloadLength | length of the payload |
| signatureBytes | the signature |
| signatureLengthB | the signature length |
| tenduke::crypto::CryptoException | if there are are cryptographic issues |
 1.17.0