 |
10Duke Enterprise C++ SDK
|
|
10Duke Enterprise C++ SDK
|
#include <LibcryptoAESCipher.h>
Libcrypto implementation of AES GCM cipher.
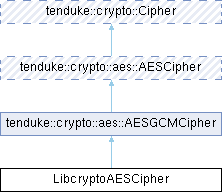
Public Member Functions | |
| LibcryptoAESCipher (const ::tenduke::crypto::aes::libcrypto::LibcryptoAESKey &key) | |
| LibcryptoAESCipher (const LibcryptoAESCipher &)=delete | |
| LibcryptoAESCipher (LibcryptoAESCipher &&other) noexcept=default | |
| LibcryptoAESCipher & | operator= (const LibcryptoAESCipher &)=delete |
| LibcryptoAESCipher & | operator= (LibcryptoAESCipher &&other) noexcept=default |
| void | decryptData (const ::tenduke::utl::DataSpan &ciphertext, ::tenduke::utl::DataSink &plaintext) const override |
| Utility method to decrypt data. | |
| void | encryptData (const ::tenduke::utl::DataSpan &plaintext, ::tenduke::utl::DataSink &ciphertext) const override |
| Utility method to encrypt data. | |
| void | encryptData (const ::tenduke::utl::DataSpan &nonce, const ::tenduke::utl::DataSpan &plaintext, ::tenduke::utl::DataSink &ciphertext) const override |
| Encrypts data using the provided nonce. | |
| Public Member Functions inherited from tenduke::crypto::aes::AESCipher | |
| AESCipher (const AESCipher &)=delete | |
| AESCipher & | operator= (const AESCipher &)=delete |
| AESCipher (AESCipher &&other) noexcept=default | |
| AESCipher & | operator= (AESCipher &&other) noexcept=default |
| Public Member Functions inherited from tenduke::crypto::Cipher | |
| Cipher (const Cipher &)=delete | |
| Cipher & | operator= (const Cipher &)=delete |
| Cipher (Cipher &&other) noexcept=default | |
| Cipher & | operator= (Cipher &&other) noexcept=default |
|
overridevirtual |
Utility method to decrypt data.
This method decrypts the provided data, encrypted by ::encryptData() method. Decrypted data is appended to plaintext only after the data has been authenticated: If decryption fails (e.g. the data has been tampered with), the method throws and plaintext is not modified.
| ciphertext | the encrypted data |
| plaintext | the decrypted data |
Implements tenduke::crypto::Cipher.
|
overridevirtual |
Encrypts data using the provided nonce.
Writes [nonce][ciphertext][authentication tag] to ciphertext.
WARNING: A (key, nonce) pair must never be used more than once. Reusing a nonce with the same key reveals the XOR of the plaintexts and allows forging authentication tags. Prefer encryptData(plaintext, ciphertext), which generates a random nonce, unless the nonce is itself a fresh random value (for example a salt that is also used for key derivation).
| nonce | the nonce (IV) to use; must be exactly GCM_NONCE_SIZE bytes |
| plaintext | data to encrypt |
| ciphertext | sink that receives the output |
| tenduke::crypto::CryptoException | if the nonce is not GCM_NONCE_SIZE bytes |
Implements tenduke::crypto::aes::AESGCMCipher.
|
overridevirtual |
Utility method to encrypt data.
This method encrypts the provided data and outputs a binary data object which contains:
| plaintext | the data to encrypt |
| ciphertext | the encrypted data |
Reimplemented from tenduke::crypto::aes::AESGCMCipher.
 1.17.0