 |
10Duke Enterprise C++ SDK
|
|
10Duke Enterprise C++ SDK
|
#include <WinCNGCiphers.h>
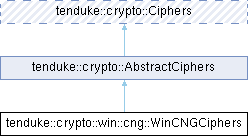
Windows CNG implementation of tenduke::crypto::Ciphers.
Provides symmetric encryption and decryption using AES-256-GCM via Windows CNG. Uses PBKDF2 with SHA-256 for key derivation. Output format: [magic (4 bytes)] [version (2 bytes)] [nonce/salt (12 bytes)] [ciphertext] [tag (16 bytes)]
Additional Inherited Members | |
| Public Member Functions inherited from tenduke::crypto::AbstractCiphers | |
| AbstractCiphers (const std::shared_ptr<::tenduke::utl::random::RandomBytes > &random, const std::shared_ptr<::tenduke::crypto::PBKDF2 > &keyGenerator) | |
| std::unique_ptr<::tenduke::utl::BinaryData > | decrypt (const ::tenduke::utl::DataSpan &ciphertext, const ::tenduke::utl::DataSpan &encryptionKey) const override |
| Decrypts given data using the system default cipher (AES256 GCM). | |
| std::string | decryptString (const ::tenduke::utl::DataSpan &ciphertext, const ::tenduke::utl::DataSpan &encryptionKey) const override |
| Decrypts given data using the system default cipher (AES256 GCM) to a string. | |
| std::unique_ptr<::tenduke::utl::BinaryData > | encrypt (const ::tenduke::utl::DataSpan &plaintext, const ::tenduke::utl::DataSpan &encryptionKey) const override |
| Encrypts given data using the system default cipher (AES256 GCM). | |
| std::unique_ptr<::tenduke::utl::BinaryData > | encrypt (const std::string &plaintext, const ::tenduke::utl::DataSpan &encryptionKey) const override |
| Encrypts given data using the system default cipher (AES256 GCM). | |
| std::string | decryptString (const ::tenduke::crypto::Cipher &cipher, const ::tenduke::utl::DataSpan &ciphertext) const override |
| Decrypts given data using the given cipher to a string. | |
| void | encrypt (const ::tenduke::crypto::Cipher &cipher, const ::tenduke::utl::DataSpan &plaintext, ::tenduke::utl::DataSink &ciphertext) const override |
| Encrypts data with the given cipher. | |
| Protected Member Functions inherited from tenduke::crypto::AbstractCiphers | |
| virtual std::unique_ptr<::tenduke::utl::BinaryData > | encryptBytes (const unsigned char *plaintext, std::size_t plaintextLength, const unsigned char *encryptionKey, std::size_t encryptionKeyLength) const |
| virtual std::unique_ptr<::tenduke::utl::BinaryData > | decryptBytes (const unsigned char *ciphertext, std::size_t ciphertextLength, const unsigned char *encryptionKey, std::size_t encryptionKeyLength) const |
| virtual void | writeHeader (unsigned char *buffer, const std::uint16_t version) const |
| virtual void | writeHeader (::tenduke::utl::DataSink &output, const std::uint16_t version) const |
| virtual std::uint16_t | readAndValidateHeader (const unsigned char *buffer, std::size_t bufferLength) const |
| virtual std::uint16_t | readAndValidateHeader (const ::tenduke::utl::DataSpan &buffer) const |
| Static Protected Attributes inherited from tenduke::crypto::AbstractCiphers | |
| static constexpr std::uint32_t | BLOB_MAGIC = 0x44554B45 |
| Magic value for encrypted blob header. | |
| static constexpr std::size_t | BLOB_HEADER_SIZE = 6 |
| Header size: magic (4 bytes) + version (2 bytes). | |
| static constexpr std::uint16_t | VERSION_1 = 0x0001 |
| static constexpr std::uint16_t | VERSION_2 = 0x0002 |
| static constexpr int | PBKDF2_ITERATIONS = 100000 |
| Number of PBKDF2 iterations for VERSION_1 key derivation. | |
 1.17.0