 |
10Duke Enterprise C++ SDK
|
|
10Duke Enterprise C++ SDK
|
#include <JWKSSignatureValidator.h>
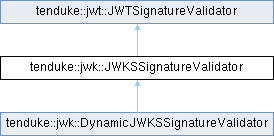
A tenduke::jwt::JWTSignatureValidator, which determines the validation key and algorithm based on the JWT header and looking up the key from memory cache.
The service maintains a (usually shared) key set, which is essentially a map. The service uses "kid"-claim from the header to lookup key from the key set. If the set does not contain the key, the token does not validate. If the header has no "kid"-claim, the key set must contain exactly one key usable for signatures, otherwise the token does not validate. If that key does not verify the signature, the key may have been rotated: subclasses can then provide a replacement key, see findRotatedJWK(). The key must be usable for verifying signatures with the validation algorithm, see tenduke::jwk::JWK::isUsableForSignature().
The service honors the "alg"-claim of the header and uses the algorithm to validate the signature (but note the validationAlgorithm constructor parameter). If the alg-claim is missing, is none or is not a supported algorithm, the token does not validate.
Public Member Functions | |
| JWKSSignatureValidator (const std::shared_ptr< tenduke::jwk::JWKS > &keySet, ::tenduke::crypto::HashAlgorithm validationAlgorithm=::tenduke::crypto::HashAlgorithm::NONE) | |
| Constructs new instance. | |
| bool | validate (const tenduke::json::JSONObject *jwtHeader, const char *payload, std::size_t payloadLength, const unsigned char *signatureBytes, std::size_t signatureLengthB) const override |
| Validates JWT signature. | |
| std::vector< std::shared_ptr< const tenduke::crypto::PublicKey > > | getVerificationKeys () const override |
| Returns the keys in the key set, which are usable for verifying signatures with the validation algorithm. | |
Protected Member Functions | |
| virtual std::unique_ptr< tenduke::jwk::JWK > | findJWK (const std::string &keyId) const |
| Locates the key from cache by id. | |
| virtual std::unique_ptr< tenduke::jwk::JWK > | findRotatedJWK (const tenduke::jwk::JWK &rejectedKey) const |
| Locates a replacement for the key, which did not verify the signature of a JWT without "kid"-claim. | |
| virtual void | mergeKeys (const tenduke::jwk::JWKS &newKeySet) const |
| Merges keys from newKeySet to the contained keySet. | |
| virtual void | replaceKeys (const tenduke::jwk::JWKS &newKeySet) const |
| Replaces keys of the contained keySet with the keys from newKeySet. | |
|
explicit |
Constructs new instance.
| keySet | - |
| validationAlgorithm | Pre-set validation algorithm to use. If set to anything else than NONE, this algorithm is ALWAYS used to validate the token. This prevents tampering the token. If NONE, the algorithm from the JWT header is used: the JWT-header must then have alg-claim which maps to supported algorithm (excluding NONE), otherwise the token does not validate. |
|
protectedvirtual |
Locates the key from cache by id.
| keyId | the key id. If empty, the only key usable for signatures is returned. |
Reimplemented in tenduke::jwk::DynamicJWKSSignatureValidator.
|
protectedvirtual |
Locates a replacement for the key, which did not verify the signature of a JWT without "kid"-claim.
A JWT without "kid" is verified with the only key usable for signatures (see findJWK()). If the key has been rotated, the JWT cannot select the new key by "kid". This hook allows e.g. refreshing the keys. This implementation does not replace keys and returns nullptr.
| rejectedKey | the key, which did not verify the signature |
Reimplemented in tenduke::jwk::DynamicJWKSSignatureValidator.
|
overridevirtual |
Returns the keys in the key set, which are usable for verifying signatures with the validation algorithm.
The keys come from the key set in memory: Nothing is loaded over the network.
Reimplemented from tenduke::jwt::JWTSignatureValidator.
|
overridevirtual |
Validates JWT signature.
| jwtHeader | JWT-header, can be e.g. used to determine the key and digestAlgorithm used |
| payload | JWT-payload to verify |
| payloadLength | length of the payload |
| signatureBytes | the signature |
| signatureLengthB | the signature length |
| tenduke::crypto::CryptoException | if there are are cryptographic issues |
Implements tenduke::jwt::JWTSignatureValidator.
 1.17.0